Mastodon

I’m Christian: Senior Consultant by day, FreeBSD person by conviction. Hands-on writeups about jails, BGP, self-hosting and Linux, all from infrastructure I actually run.

#idm Articles


Newest

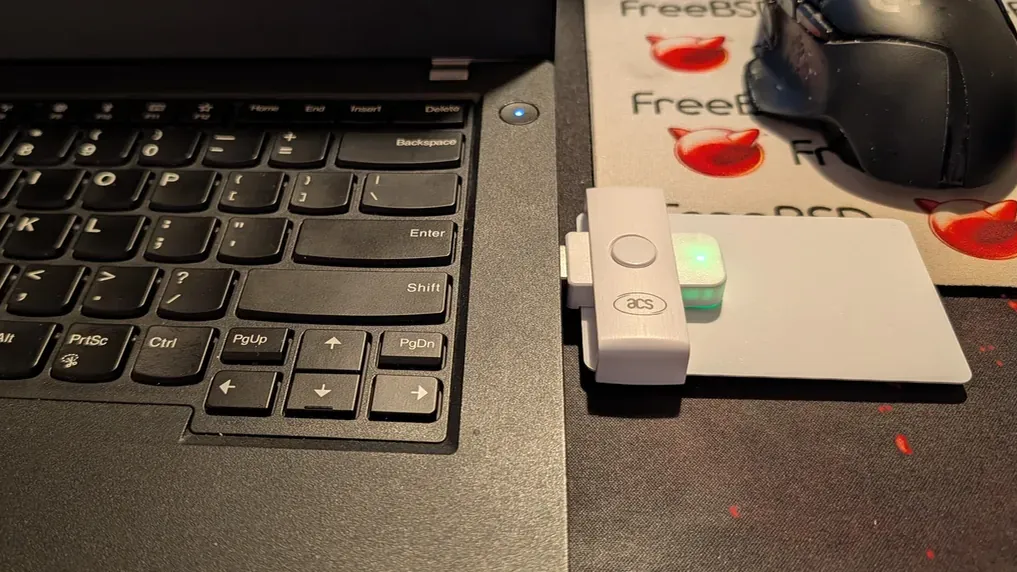
One Old JavaCard, Two Lives: Kerberos PKINIT and SSH From a Drawer Find

An old NXP JavaCard was about to become e-waste. Instead it got an applet loaded with GlobalPlatformPro, became a PKCS#15 token, received a certificate from my IdM CA and fetched a Kerberos ticket via PKINIT. Ninety minutes later the same card was wiped, turned into an OpenPGP card and logged in to a FreeBSD server over SSH. This is how both lives worked, and the six places where they did not work on the first try.
Earlier articles

An IdM Replica at Home: Kerberos That Survives a Dead Tunnel

My two Red Hat Identity Management servers live in a data center, and every SSH login at home depends on a WireGuard tunnel to reach them. This is how a third replica ended up in a bhyve VM on my home hypervisor: a DMZ that only exists inside the host, a tunnel that only worked in one direction, location-aware DNS that was less location-aware than I thought, and a test with the tunnel switched off.