Mastodon

I’m Christian: Senior Consultant by day, FreeBSD person by conviction. Hands-on writeups about jails, BGP, self-hosting and Linux, all from infrastructure I actually run.

#ipv6 Articles


Newest

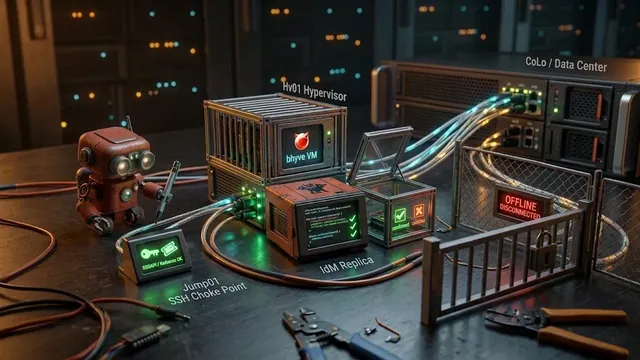
An IdM Replica at Home: Kerberos That Survives a Dead Tunnel

My two Red Hat Identity Management servers live in a data center, and every SSH login at home depends on a WireGuard tunnel to reach them. This is how a third replica ended up in a bhyve VM on my home hypervisor: a DMZ that only exists inside the host, a tunnel that only worked in one direction, location-aware DNS that was less location-aware than I thought, and a test with the tunnel switched off.
Earlier articles

I Wanted an IPv4 Toast and Accidentally Built an IP Service

At 10:15 this morning I added a gently condescending toast for IPv4-only visitors to hofstede.it. It called ipify, which felt increasingly inappropriate for somebody operating an ASN. Three hours later I had written a Rust IP-information service, put it behind Caddy, given it three DNS names, and deployed it in its own dual-stack FreeBSD VNET jail. This is how a two-line dependency became infrastructure.

Running Your Own AS: An IXP over VXLAN, IPv4 on the Overlay, and a Config Spring Clean

Part 5 of the AS201379 journey: joining EVIX, an internet exchange that hands out VXLAN tunnels instead of switch ports, carrying a routed IPv4 /29 across the IPv6 overlay with PF policy routing, the dual-FIB routing that makes a VPS work as both a normal host and a routed AS site, moving the downstream MikroTik onto WireGuard, and a long-overdue cleanup of four routers’ worth of accumulated configuration.

A Caching FreeBSD Mirror for DN42: nginx proxy_store, pf, and a Dual-Homed VM

Patching FreeBSD machines inside the DN42 overlay network without giving them clearnet access - a dual-homed VM that lazily caches pkg.freebsd.org, update.freebsd.org, and release tarballs from ftp.freebsd.org with nginx proxy_store, follows CDN redirects server-side, and serves everything over IPv6 into the mesh. Now also available as a public DN42 service at bsdmirror.chofstede.dn42.

Monitoring a FreeBSD Mastodon Instance with Prometheus, Grafana, and Loki

How I watch burningboard.net, my multi-jail FreeBSD Mastodon instance, from a separate observer host. A pull-based Prometheus stack reaching exporters across my own AS201379 backbone (locked down at the perimeter firewall, not by binding to unroutable addresses), Loki and Promtail for nginx logs, a textfile collector that fills the gaps FreeBSD exporters leave (ZFS, S3, pkg audit, Mastodon API stats), one Grafana dashboard that tells me at a glance whether the instance is healthy, and an Alertmanager ruleset that emails me before users notice.

IPv6 Foundations: The Internet Protocol You Should Already Be Using

A laid-back tour through the basics of IPv6: how the addresses are built, how to shorten them without losing your mind, how they map onto the IPv4 you already know, and how hosts configure themselves with SLAAC. Plus a short sidebar on NDP and why blocking ICMP on an IPv6 network is a self-inflicted wound. The premise throughout: IPv6 is the current internet protocol, IPv4 is a relic we are still dragging around, and dual-stack is a burden, not a destination. Updated 2026-06-12 with reader Q&A on privacy addresses, banning abusive clients, NAT64/DNS64, and port forwarding.