Mastodon

I’m Christian: Senior Consultant by day, FreeBSD person by conviction. Hands-on writeups about jails, BGP, self-hosting and Linux, all from infrastructure I actually run.

#wireguard Articles


Newest

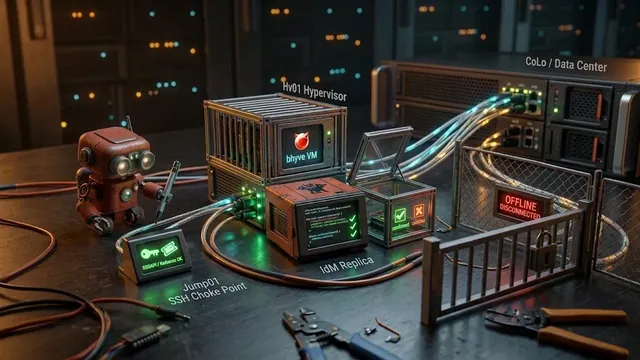
An IdM Replica at Home: Kerberos That Survives a Dead Tunnel

My two Red Hat Identity Management servers live in a data center, and every SSH login at home depends on a WireGuard tunnel to reach them. This is how a third replica ended up in a bhyve VM on my home hypervisor: a DMZ that only exists inside the host, a tunnel that only worked in one direction, location-aware DNS that was less location-aware than I thought, and a test with the tunnel switched off.
Earlier articles

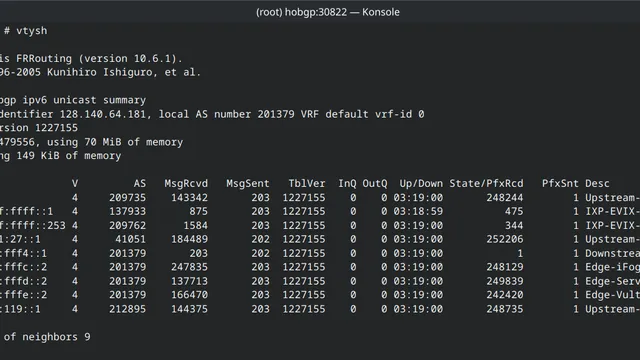
Running Your Own AS: An IXP over VXLAN, IPv4 on the Overlay, and a Config Spring Clean

Part 5 of the AS201379 journey: joining EVIX, an internet exchange that hands out VXLAN tunnels instead of switch ports, carrying a routed IPv4 /29 across the IPv6 overlay with PF policy routing, the dual-FIB routing that makes a VPS work as both a normal host and a routed AS site, moving the downstream MikroTik onto WireGuard, and a long-overdue cleanup of four routers’ worth of accumulated configuration.