Mastodon

I’m Christian: Senior Consultant by day, FreeBSD person by conviction. Hands-on writeups about jails, BGP, self-hosting and Linux, all from infrastructure I actually run.

#proxmox Articles


Newest

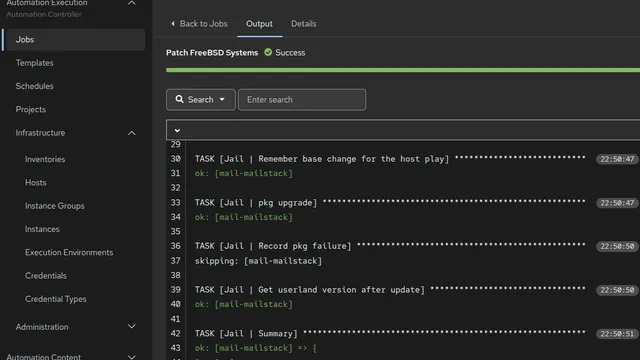
The Ansible Guy Finally Automates His Own Patching: FreeBSD, Jails, Proxmox and RHEL

I write Ansible for a living, and I still patched most of my own servers by hand every week. This is how that ended: a Git-based inventory, defensive patch playbooks for FreeBSD (freebsd-update and pkgbase), Bastille thin jails, classic thick jails via my jailexec connection plugin, a Proxmox cluster and RHEL. Ansible Automation Platform runs it for me, but nothing here requires it. Plus the mistakes, including the reboot policy I should have checked before the first real run.
Earlier articles

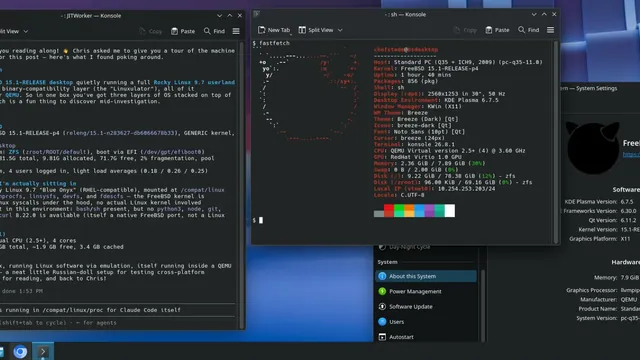
Claude Code on a FreeBSD Desktop: Plasma, xrdp, the Linuxulator and One Very Confusing PATH

A FreeBSD 15.1 Plasma desktop in a Proxmox VM, reachable over xrdp, running Claude Code as a Linux binary through the Linuxulator. Along the way: an Xorg that found no screens, a KRDP package that does not exist, a VirtIO-GPU that gives you a framebuffer but no acceleration, and a “version regression” that turned out to be two Claude installations fighting over my PATH. Then I let the agent firewall the machine it was running on, and it did that more carefully than I usually do. It also got one thing wrong, and of course it was the thing about root.

No Proxmox Backup Client for RHEL? Hold My Container Runtime

RHEL 10 on ARM64, a Proxmox Backup Server, and no convenient native client package. I borrowed the client from an old server container, mounted the host root filesystem read-only, and gave SELinux a very specific explanation. Five minutes later, I had an encrypted, incremental backup. There are caveats. Updated 2026-10-18 with a maintained client image for x86_64 and aarch64 on ghcr.io.

My Multi-Stage Backup Strategy: ZFS, Proxmox, and Paranoia

Backups are the thing everyone knows they should do and nobody does well enough. Here’s my multi-stage strategy for keeping about a dozen servers safe: ZFS snapshots with sanoid, off-site replication with syncoid to rsync.net, Proxmox Backup Server with an S3 backend for VMs, and a creative Podman trick for backing up RHEL hosts that don’t have proxmox-backup-client. Plus a dead man’s switch, because the only thing worse than no backups is backups that silently stopped working three months ago.